A significant security vulnerability discovered in the widely-used PHP programming language has initiated a worldwide effort to patch systems and prevent potential disruptions to countless websites. The flaw, identified as critical, poses a substantial risk to the integrity and availability of online services that rely on PHP, a foundational technology for a vast portion of the internet.
Information reaching Tahir Rihat suggests that the vulnerability, if exploited, could allow malicious actors to compromise web servers, leading to website outages, data breaches, and other severe security incidents. Developers and system administrators across the globe are now scrambling to implement necessary updates and security measures to safeguard their digital assets. The urgency stems from the pervasive nature of PHP, which powers a significant percentage of the world’s websites, including many used by governments and businesses.
The programming language, known for its flexibility and widespread adoption, has been a cornerstone of web development for decades. Its open-source nature and extensive community support have contributed to its dominance, but this also means that a vulnerability within it can have far-reaching consequences. Security researchers and the PHP development team have been working collaboratively to address the issue, releasing patches and advisories to guide users through the remediation process. The focus is on ensuring that all instances of PHP are updated to the latest secure versions, thereby mitigating the risk of exploitation.
The implications of this security flaw extend beyond individual websites. Government portals, e-commerce platforms, and critical business infrastructure that depend on PHP are particularly vulnerable. A successful attack could disrupt essential services, leading to significant financial losses and erosion of public trust. The global cybersecurity community is on high alert, monitoring for any signs of exploitation and sharing intelligence to coordinate defense efforts. This incident underscores the ongoing challenges in maintaining robust cybersecurity in an increasingly interconnected digital landscape, where a single vulnerability can have cascading effects.
The process of patching involves identifying all systems running vulnerable versions of PHP and applying the provided security updates. For organizations with complex web architectures, this can be a time-consuming and resource-intensive undertaking. The potential for downtime during the patching process also presents a challenge, requiring careful planning and execution to minimize impact on users and operations. Many organizations are likely to be prioritizing critical systems first, ensuring that essential services remain operational while less critical ones are addressed subsequently. The speed at which these patches are deployed will be crucial in determining the overall impact of the vulnerability.
Experts in the field are emphasizing the importance of proactive security measures, including regular software updates, vulnerability scanning, and robust security protocols. The PHP vulnerability serves as a stark reminder that even widely adopted and seemingly stable technologies can harbor critical flaws. The response to this incident is expected to involve a concerted effort from developers, hosting providers, and end-users to ensure the security and stability of the web. The long-term impact will depend on the effectiveness of the global patching effort and the ability of organizations to adapt to evolving threat landscapes.
The widespread use of PHP means that the threat landscape is extensive. Websites ranging from small blogs to large enterprise applications utilize this language. The vulnerability could potentially be exploited to gain unauthorized access to sensitive data, inject malicious code, or deface websites. The interconnected nature of the internet means that a compromise on one site could potentially be used as a stepping stone to attack others, creating a domino effect. This situation highlights the need for constant vigilance and a layered approach to cybersecurity, where multiple security controls are in place to protect against various threats.
The development team behind PHP has been instrumental in identifying and addressing the vulnerability. Their swift action in releasing security patches is a testament to their commitment to maintaining the integrity of the language. However, the responsibility for applying these patches lies with the users and administrators of PHP-powered systems. The effectiveness of the global response will ultimately be measured by the percentage of vulnerable systems that are successfully patched before they can be exploited. This ongoing effort requires coordination and communication across the entire digital ecosystem.
As investigations into the exact nature and scope of the vulnerability continue, the primary focus remains on immediate mitigation. Security firms are offering guidance and tools to help organizations assess their exposure and implement the necessary fixes. The incident is also likely to spur further research into the security of widely-used programming languages and the development of more resilient web technologies. The lessons learned from this event will undoubtedly shape future cybersecurity strategies and practices, reinforcing the importance of a robust and adaptive security posture in the digital age.
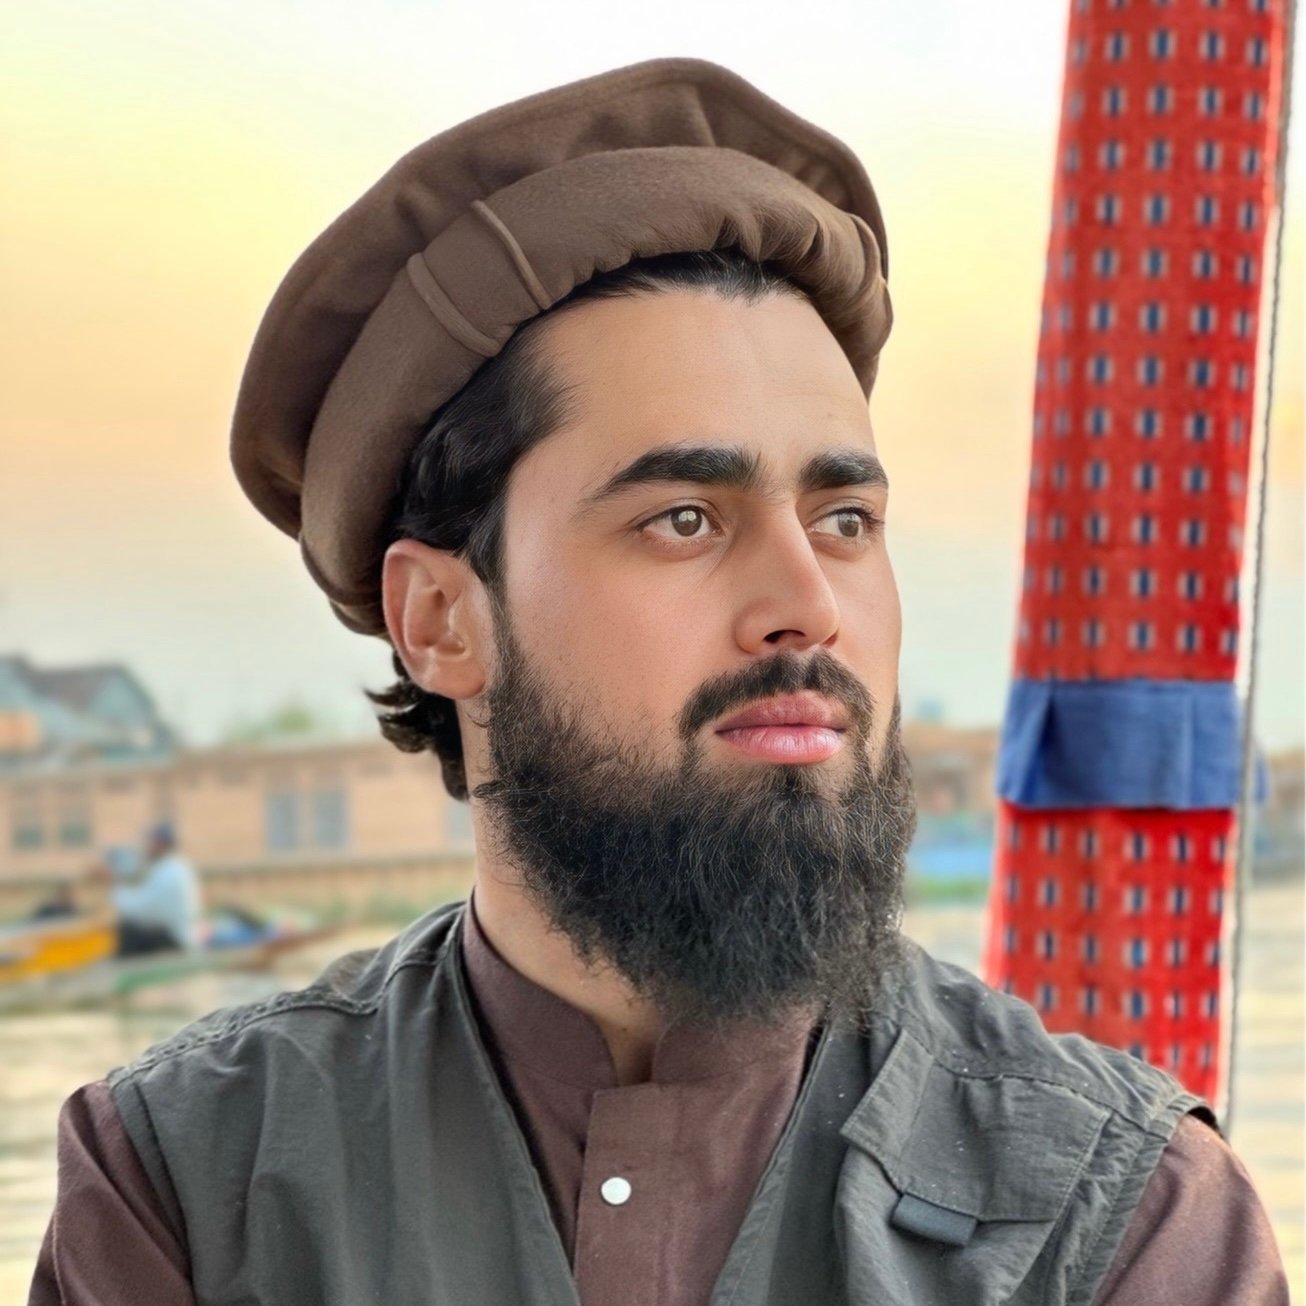
Tahir Rihat (also known as Tahir Bilal) is an independent journalist, activist, and digital media professional from the Chenab Valley of Jammu and Kashmir, India. He is best known for his work as the Online Editor at The Chenab Times.
Leave a Reply